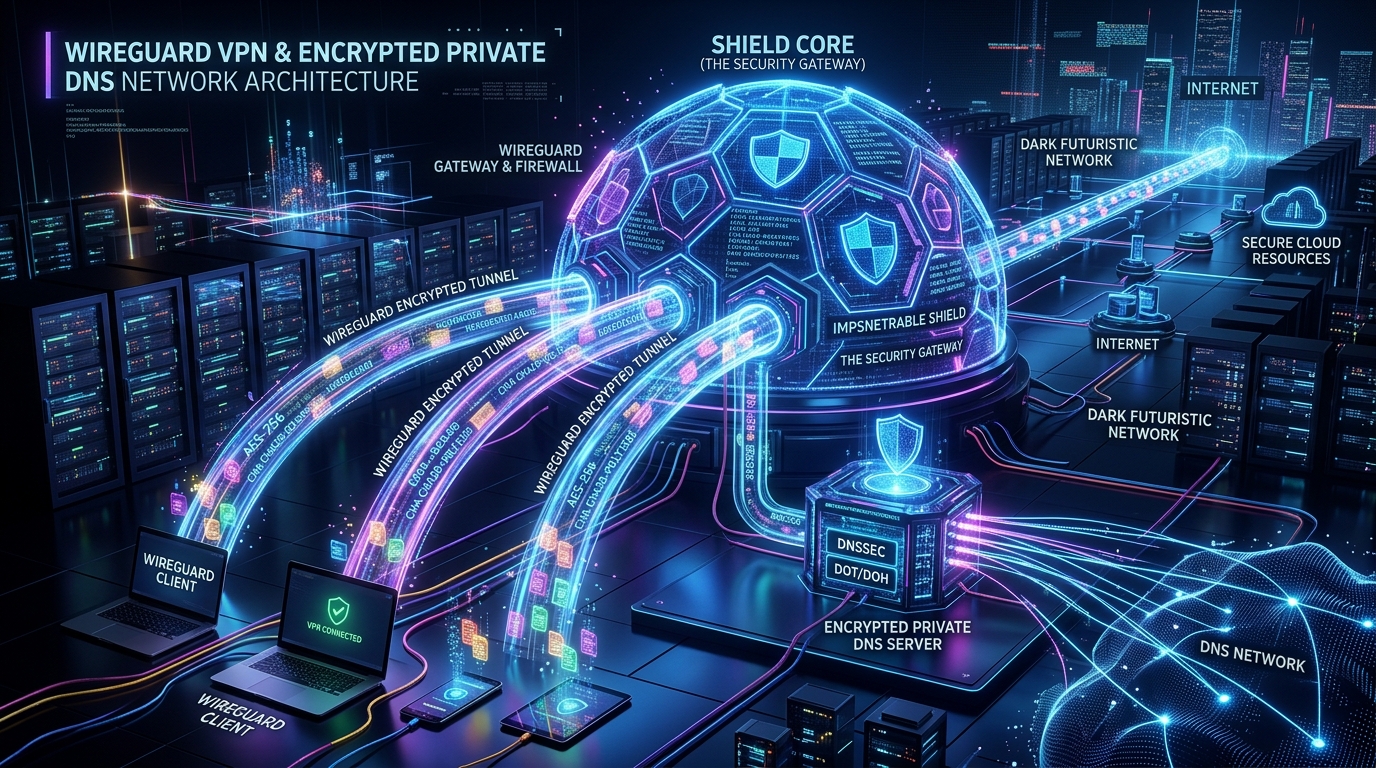
Commercial VPN providers frequently market "anonymity," but in practice, you are simply shifting your trust—and your unencrypted DNS requests—from your local Internet Service Provider (ISP) to a third-party corporation whose logging practices and ownership structures are often opaque.
By self-hosting your own WireGuard VPN on an inexpensive cloud VPS (DigitalOcean, Hetzner, Linode, or AWS) and pairing it with a private, recursive Unbound DNS resolver, you gain absolute control over your network traffic: end-to-end cryptographic encryption, blazing kernel-level throughput, zero ISP tracking, and automatic network-wide ad/telemetry blocking.
In this comprehensive guide, we walk through the complete production setup: configuring WireGuard in the Linux kernel, enabling IP forwarding and firewall NAT masquerading, pairing with Unbound recursive DNS, and generating 1-second mobile onboarding QR codes.
Why WireGuard Outclasses Legacy VPNs (OpenVPN / IPsec)
| Architectural Metric | Legacy OpenVPN | Modern WireGuard |
|---|---|---|
| Kernel vs. User Space | User-space daemon (Heavy context switching between kernel & user space). | In-Kernel Module (Near line-rate hardware network speed). |
| Codebase Complexity | ~70,000 to 100,000 lines of code (Large attack surface). | ~4,000 lines of code (Easily auditable, minimal attack surface). |
| Cryptographic Primitives | Negotiated ciphers (Vulnerable to cipher downgrade attacks). | Modern fixed cipher suite: Curve25519, ChaCha20-Poly1305, BLAKE2s. |
| Roaming & Disconnects | Drops connections during Wi-Fi ↔ 5G handoffs, requiring renegotiation. | Seamless roaming: uses Cryptokey Routing based on public keys without dropping sessions. |
Step 1: Installing WireGuard & Enabling Kernel IP Forwarding
On your clean Ubuntu / Debian Linux VPS:
# 1. Update packages and install WireGuard & QR code generator
sudo apt update && sudo apt install -y wireguard qrencode unbound

# 2. Enable IPv4 and IPv6 packet forwarding in the Linux Kernel
sudo tee /etc/sysctl.d/99-wireguard-forwarding.conf <<EOF
net.ipv4.ip_forward = 1
net.ipv6.conf.all.forwarding = 1
EOF

# Apply sysctl changes immediately
sudo sysctl -p /etc/sysctl.d/99-wireguard-forwarding.conf
Step 2: Generating Cryptographic Server & Client Keys
# Create secure directory with restricted permissions
umask 077
mkdir -p /etc/wireguard/keys

# Generate Server Private and Public Keys
wg genkey | tee /etc/wireguard/keys/server_private.key | wg pubkey > /etc/wireguard/keys/server_public.key

# Generate First Client (e.g., iPhone) Private and Public Keys
wg genkey | tee /etc/wireguard/keys/phone_private.key | wg pubkey > /etc/wireguard/keys/phone_public.key
Step 3: Configuring the Server Gateway (/etc/wireguard/wg0.conf)
Find your public network interface using ip -br route show default (typically eth0 or enp1s0):
[Interface]
Address = 10.8.0.1/24, fd42:42:42::1/64
ListenPort = 51820
PrivateKey = <SERVER_PRIVATE_KEY>

# Firewall Rules: NAT Masquerade on start, cleanup on stop
PostUp = iptables -A FORWARD -i wg0 -j ACCEPT; iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE; ip6tables -A FORWARD -i wg0 -j ACCEPT; ip6tables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
PostDown = iptables -D FORWARD -i wg0 -j ACCEPT; iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE; ip6tables -D FORWARD -i wg0 -j ACCEPT; ip6tables -t nat -D POSTROUTING -o eth0 -j MASQUERADE

# --- Client 1: iPhone ---
[Peer]
PublicKey = <PHONE_PUBLIC_KEY>
AllowedIPs = 10.8.0.2/32, fd42:42:42::2/128
Step 4: Configuring Unbound as a Local Recursive Encrypted DNS Resolver
Instead of routing DNS queries to Google (8.8.8.8) or Cloudflare (1.1.1.1), Unbound queries the authoritative root DNS servers directly from your VPS—eliminating middleman logging.
Create /etc/unbound/unbound.conf.d/wireguard-dns.conf:
server:
    verbosity: 1
    interface: 10.8.0.1
    port: 53
    do-ip4: yes
    do-ip6: yes
    do-udp: yes
    do-tcp: yes

    # Allow WireGuard VPN subnet queries only
    access-control: 10.8.0.0/24 allow
    access-control: fd42:42:42::/64 allow
    access-control: 127.0.0.1 allow

    # Security & DNSSEC Hardening
    harden-glue: yes
    harden-dnssec-stripped: yes
    use-caps-for-id: yes
    edns-buffer-size: 1232
    prefetch: yes
    prefetch-key: yes
    hide-identity: yes
    hide-version: yes
# Restart Unbound resolver
sudo systemctl restart unbound
sudo systemctl enable unbound
Step 5: Starting WireGuard and Generating Client QR Code
# Enable and start WireGuard wg0 interface
sudo systemctl enable --now wg-quick@wg0

# Inspect live interface status and handshakes
sudo wg show
Generating Mobile Profile (iphone.conf)
[Interface]
PrivateKey = <PHONE_PRIVATE_KEY>
Address = 10.8.0.2/24, fd42:42:42::2/64
# Route all DNS through your secure Unbound resolver
DNS = 10.8.0.1

[Peer]
PublicKey = <SERVER_PUBLIC_KEY>
Endpoint = YOUR_VPS_PUBLIC_IP:51820
# Route 100% of Internet traffic through the encrypted tunnel
AllowedIPs = 0.0.0.0/0, ::/0
PersistentKeepalive = 25
To import the configuration to your mobile device instantly:
qrencode -t ansiutf8 < iphone.conf
Open the WireGuard app on iOS or Android, tap "+" → "Scan from QR code", and you are instantly connected to your private, encrypted, ad-free cloud gateway!
Security & Maintenance Checklist
- ✓ Enable UFW Firewall: Allow only port
51820/udpand your hardened SSH port. Keep port 53 closed to the public internet (accessible strictly viawg0interface). - ✓ PersistentKeepalive: Always set
PersistentKeepalive = 25on mobile clients to maintain tunnel connectivity through cellular NAT firewalls. - ✓ Enable Unattended Security Updates: Run
sudo apt install unattended-upgradesto automatically patch Linux kernel security vulnerabilities.
Conclusion
Self-hosting WireGuard gives you the ultimate combination of speed, security, and true network sovereignty. With in-kernel routing and private recursive DNS resolution, your passwords, browsing history, and network queries remain completely shielded from coffee shop Wi-Fi snooping, ISP surveillance, and corporate tracking.