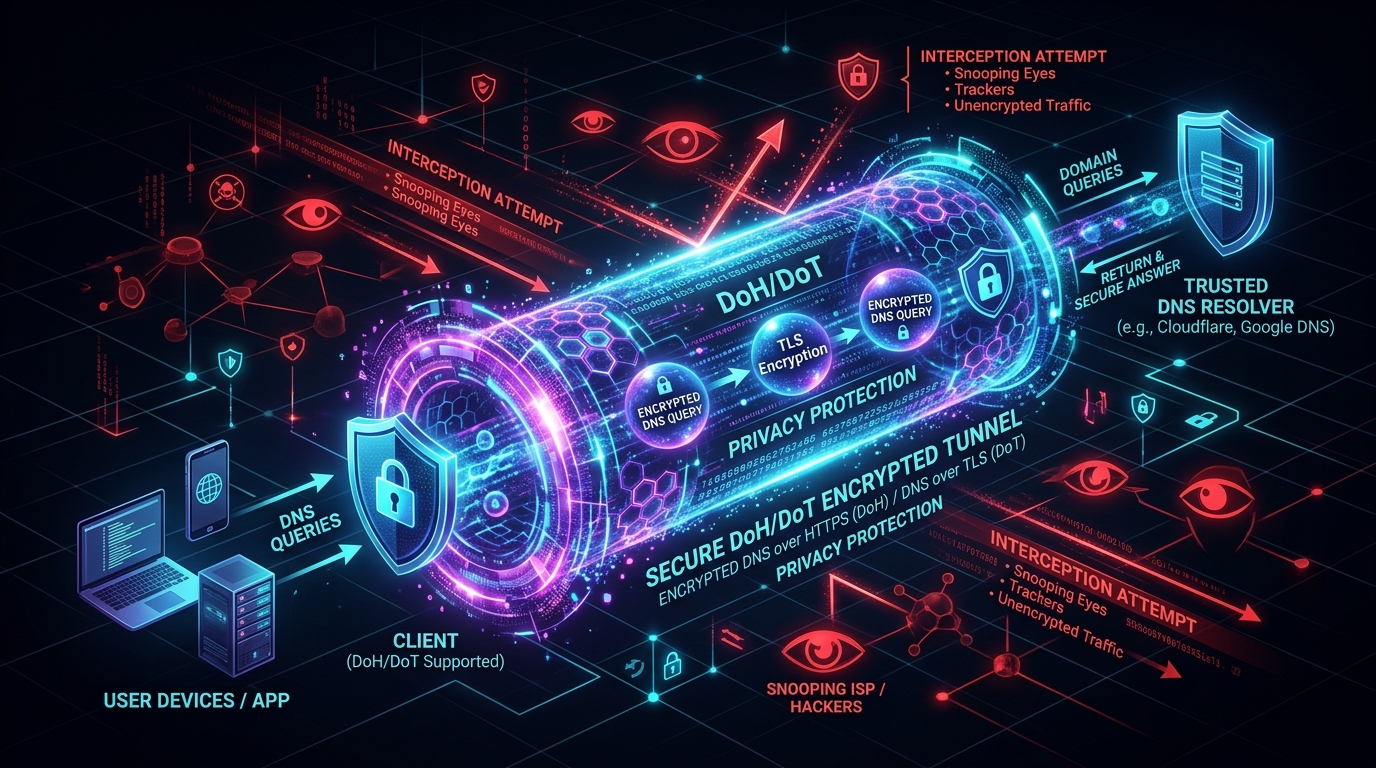
Whenever you type a web address into your browser, the first thing your device does is resolve that domain name into an IP address using the Domain Name System (DNS). Historically, this fundamental lookup has occurred over plaintext UDP on port 53—leaving a massive visibility gap in modern web privacy.
Even if every website you visit enforces HTTPS encryption, your internet service provider (ISP), local Wi-Fi hotspots, network routers, and middleboxes can eavesdrop on every single domain query in cleartext. They see the exact banking portals, healthcare websites, media platforms, and private services you access throughout the day.
To eliminate this vulnerability, the internet architecture community developed two modern encrypted DNS standards: DNS-over-HTTPS (DoH, RFC 8484) and DNS-over-TLS (DoT, RFC 7858). In this deep dive, we explore how both protocols work, compare their security characteristics, and walk through deploying system-wide DNS encryption on Linux and local networks.
The Cleartext Achilles' Heel of Traditional DNS
When DNS was designed in 1983, internet traffic was assumed to flow across cooperative, trusted networks. Port 53 lookups lack any authentication or encryption. This leaves users exposed to three primary threats:
- ISP Profiling and Ad Monetization: ISPs routinely aggregate and sell consumer DNS query records to marketing databases and data brokers.
- DNS Spoofing / Cache Poisoning: Attackers on compromised local networks or untrusted public Wi-Fi can forge DNS responses, redirecting users to malicious phishing portals.
- Government Surveillance and Censorship: Transparent DNS interception allows oppressive firewalls to hijack queries and block access to independent media.
DoH vs. DoT: Understanding the Protocols
| Specification | DNS-over-HTTPS (DoH) | DNS-over-TLS (DoT) |
|---|---|---|
| Standard | RFC 8484 | RFC 7858 |
| Port | 443 (Standard HTTPS) |
853 (Dedicated TLS Port) |
| Protocol Layer | Encapsulated in HTTP/2 or HTTP/3 over TLS | Direct TLS tunnel over TCP |
| Blockability | Very difficult (Indistinguishable from normal web traffic) | Easy (Block port 853) |
| Primary Use Case | Browsers, applications, restricted networks | System resolvers, routers, mobile OS (Android Private DNS) |
Implementing Encrypted DNS: Step-by-Step
1. Browser-Level DoH (Zero Installation)
Modern browsers allow you to enable DoH directly without modifying operating system files:
- Mozilla Firefox: Settings → Privacy & Security → DNS over HTTPS → Select Max Protection (choose Cloudflare, NextDNS, or a custom DoH endpoint).
- Google Chrome / Brave: Settings → Privacy and Security → Security → Enable Use secure DNS.
2. System-Wide DoT on Linux via systemd-resolved
Most modern Linux distributions (Ubuntu, Debian, Fedora, Arch) use systemd-resolved as their local DNS manager. You can enable native DNS-over-TLS in minutes.
Edit /etc/systemd/resolved.conf:
[Resolve]
DNS=1.1.1.1#cloudflare-dns.com 1.0.0.1#cloudflare-dns.com 2606:4700:4700::1111#cloudflare-dns.com
FallbackDNS=9.9.9.9#dns.quad9.net 149.112.112.112#dns.quad9.net
DNSOverTLS=yes
DNSSEC=yes
Cache=yes
Restart the service and flush local state:
sudo systemctl restart systemd-resolved
sudo resolvectl flush-caches
Check the active encryption status:
resolvectl status
Under the active interface, you will see +DNSOverTLS and +DNSSEC confirmed active.
3. Running a Dedicated Local DoH Proxy with cloudflared
For servers or home servers (like Raspberry Pi running Pi-hole), the cloudflared daemon provides a rock-solid local DoH proxy listening on 127.0.0.1:5053.
# Install cloudflared on Debian/Ubuntu
sudo mkdir -p --mode=0755 /etc/apt/keyrings
curl -fsSL https://pkg.cloudflare.com/cloudflare-main.gpg | sudo tee /etc/apt/keyrings/cloudflare-main.gpg >/dev/null
echo "deb [signed-by=/etc/apt/keyrings/cloudflare-main.gpg] https://pkg.cloudflare.com/cloudflared $(lsb_release -cs) main" | sudo tee /etc/apt/sources.list.d/cloudflared.list

sudo apt update && sudo apt install -y cloudflared
Configure /etc/default/cloudflared:
CLOUDFLARED_OPTS="--port 5053 --upstream https://1.1.1.1/dns-query --upstream https://1.0.0.1/dns-query"
Start and enable the daemon:
sudo systemctl enable --now cloudflared
Test resolution through your local encrypted tunnel:
dig @127.0.0.1 -p 5053 sejan.dev +short
Verifying Your Encrypted DNS & Leak Tests
To confirm that plaintext DNS requests are no longer escaping to your ISP:
- Visit 1.1.1.1/help or DNSLeakTest.com.
- Run an Extended Test.
- Verify that the resolving servers belong exclusively to your chosen encrypted resolver (e.g., Cloudflare, Quad9, NextDNS) and that your ISP's name never appears in the test output.
Summary
Deploying DNS-over-HTTPS and DNS-over-TLS closes one of the oldest plaintext vulnerabilities on the modern internet. By coupling encrypted DNS with DNSSEC validation, you ensure that every network lookup remains confidential, tamper-proof, and shielded from passive ISP data aggregation.